Firewall Rules (May 2026)#
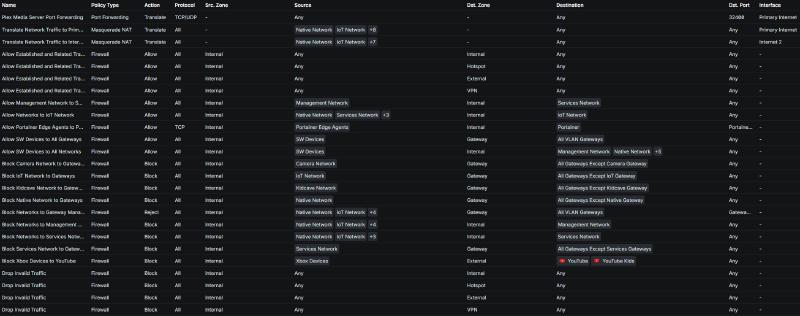
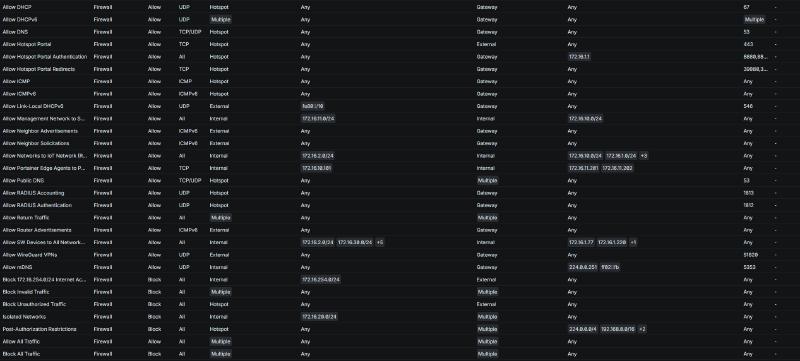
This firewall ruleset is designed around role-based access rather than flat network access. Each VLAN is treated according to its purpose, trust level, and required communication paths.
The rules allow normal return traffic first, then apply specific allow rules for approved communication such as DNS, DHCP, mDNS, WireGuard VPN, hotspot services, SW Devices access, and Management-to-Services access. Broader block and reject rules are placed below these exceptions to prevent unnecessary movement between networks.
Administrative access is restricted heavily. Non-management networks are blocked from reaching gateway management interfaces, and most VLANs are prevented from accessing other gateway addresses except their own. This helps keep IoT, Camera, Kidcave, Native, Services, and guest traffic away from router and VLAN management portals. Trusted SW Devices receive broader access for administration and troubleshooting, but that access is intentionally scoped to known devices rather than every client on the LAN.
Broad overview of current firewall ruleset below.